This article explains CMMC, the Department of Defense cybersecurity certification framework, including its three levels and the 2026 Phase 2 suspension.
Why it matters: DoD contractors and subcontractors handling FCI or CUI must still meet CMMC requirements to win and keep defense contracts, even during the current review.
Key Takeaways
- CMMC compliance protects sensitive DoD data: CMMC requires defense contractors to prove, through self-assessment or third-party review, that they safeguard federal and controlled information.
- CMMC Phase 2 is suspended, not canceled: DoD paused third-party CMMC Level 2 and 3 assessments on July 13, 2026 for a 60-day review; NIST SP 800-171 stays mandatory.
- Compliance costs are climbing fast: 46% of contractors report CMMC costs of $100K-$249K so far; Deltek Costpoint GCCM helps contractors meet certification requirements.
What Is CMMC?
CMMC stands for Cybersecurity Maturity Model Certification and is a mandatory requirement for government contractors to demonstrate that they protect sensitive government data. This requirement was introduced in 2020 by the Department of Defense. The goal of CMMC is to close cybersecurity gaps that have left the Defense Industrial Base exposed to cyberattacks.
Driven by industry feedback, the CMMC framework has been refined over time, resulting in updates to its requirements, assessment processes and maturity levels.
The latest version, previously referred to as CMMC 2.0 (and now just CMMC), was announced on November 4, 2021. The changes are intended to reduce barriers to compliance for small and mid-sized firms while maintaining the goal of protecting the Defense Industrial Base from cyberattacks.
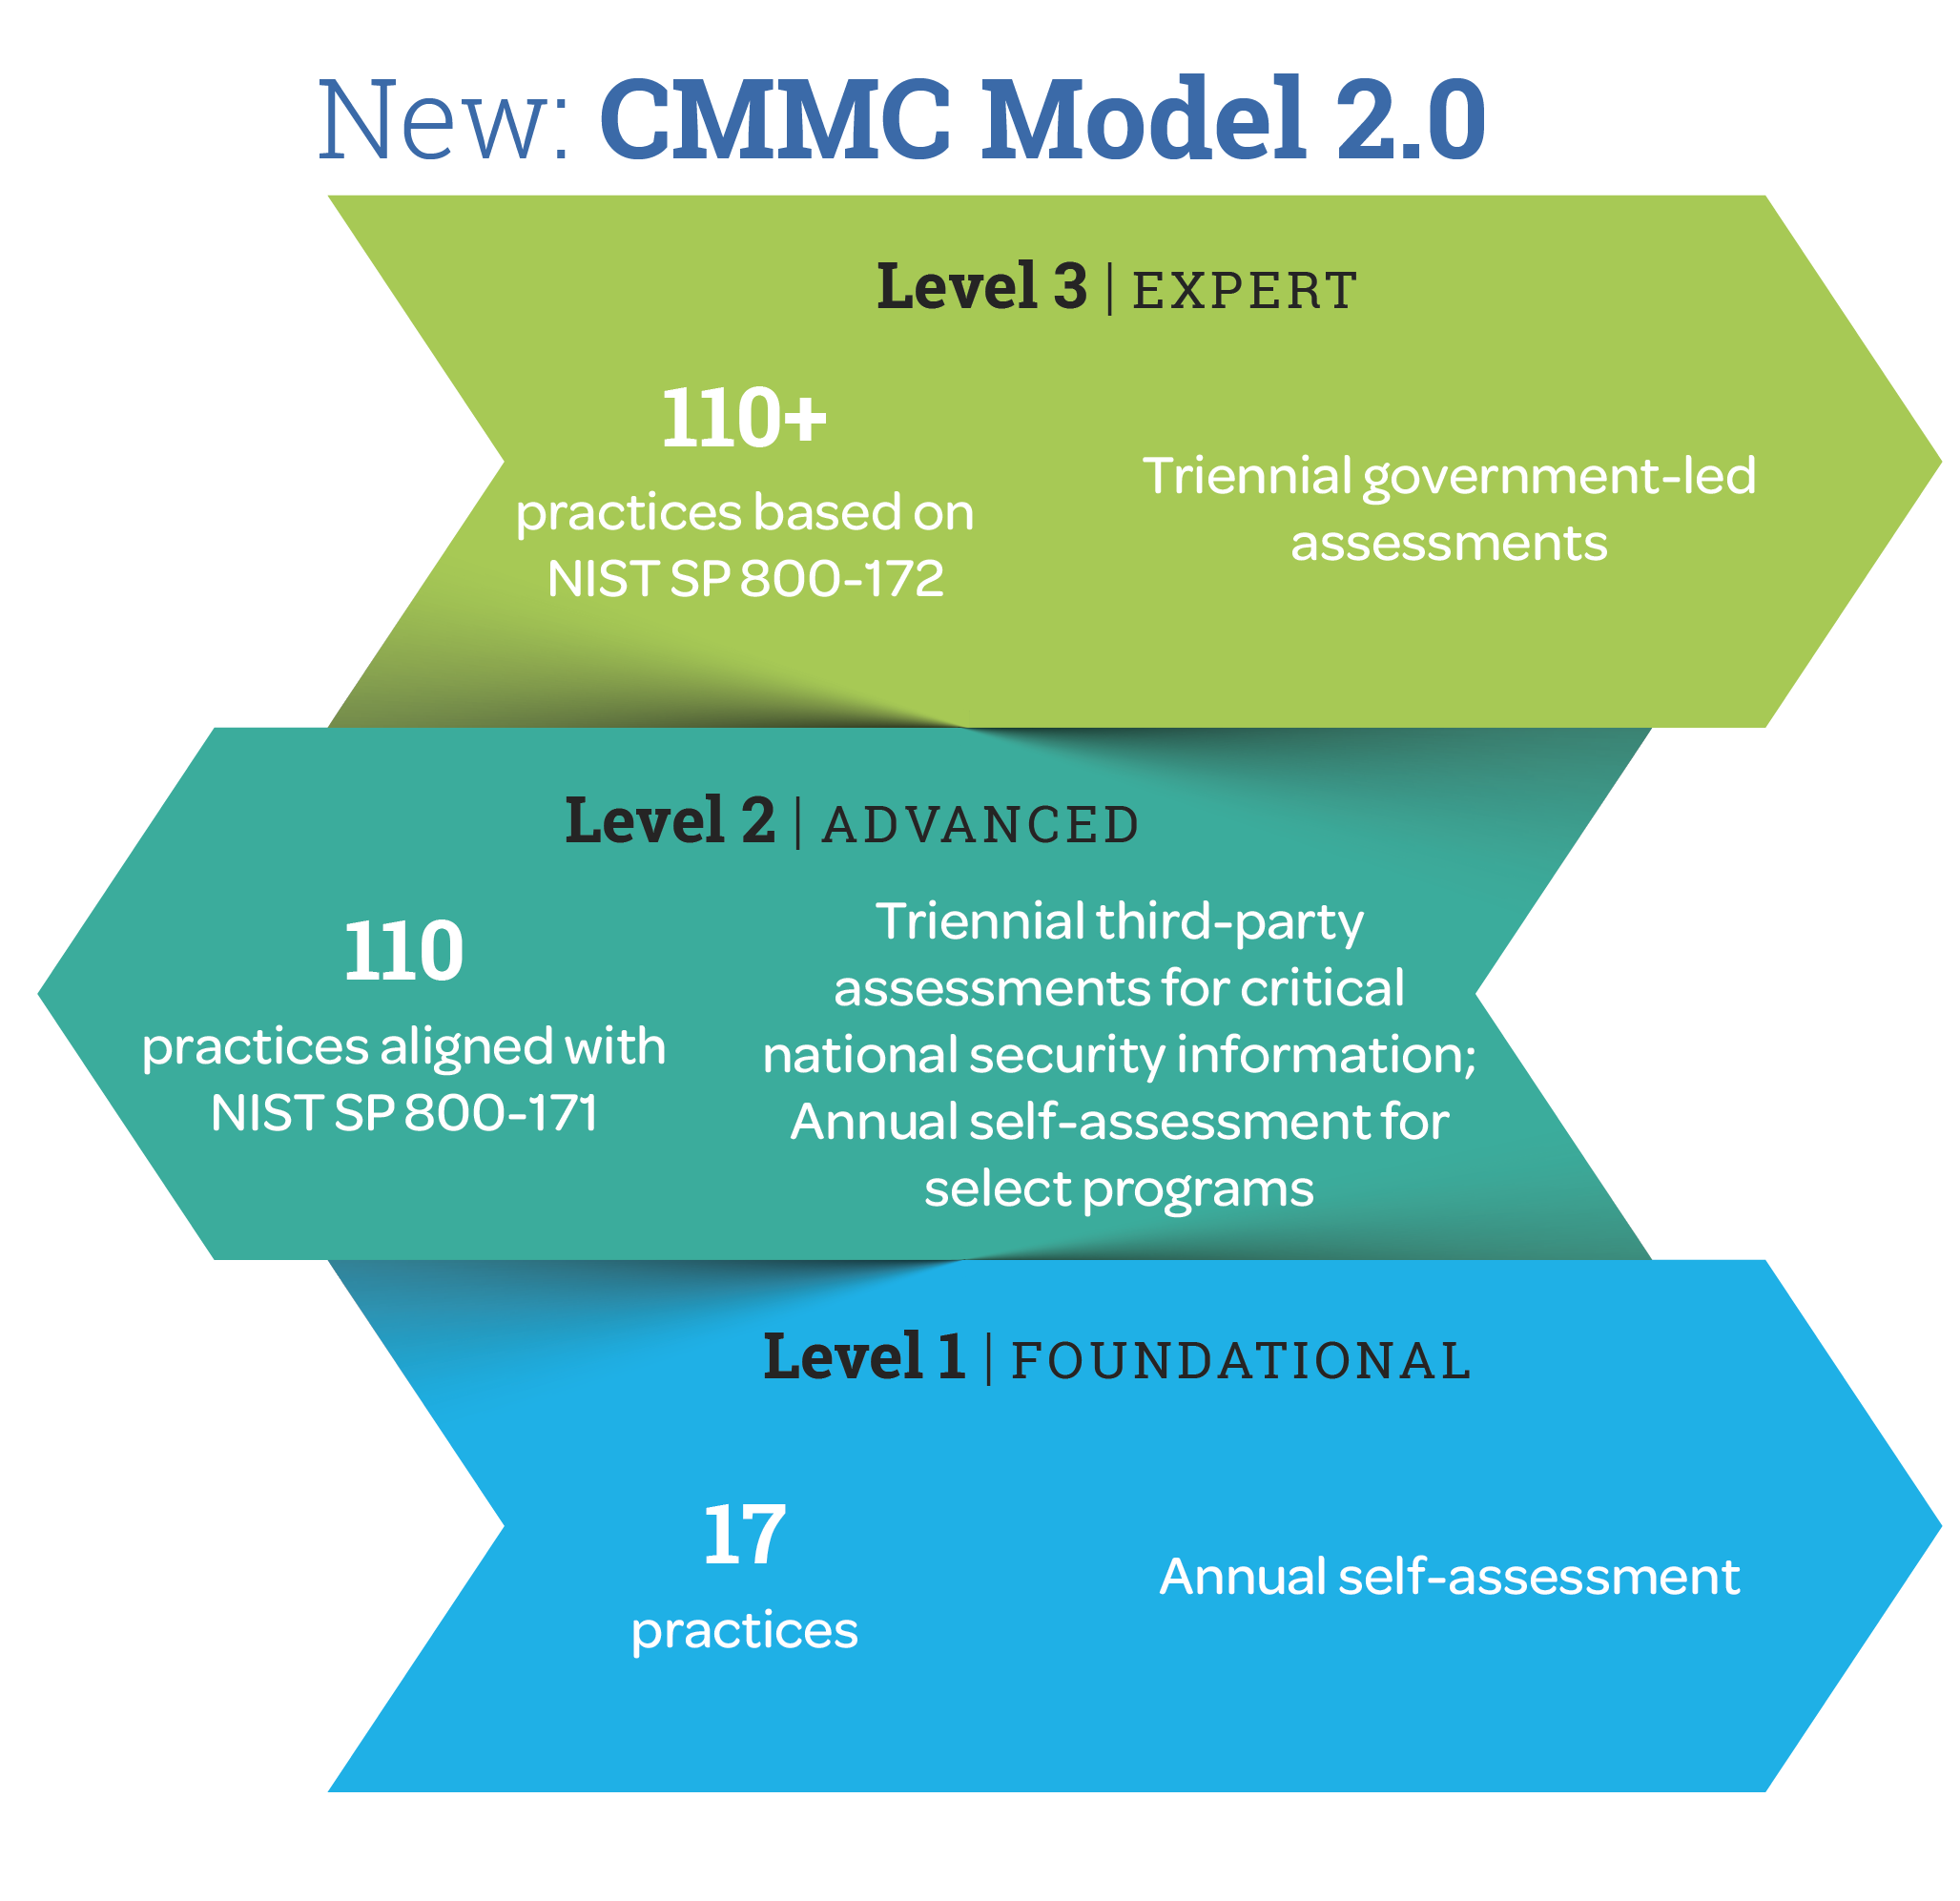
CMMC now focuses on the most critical requirements and the model has been streamlined from 5 to 3 compliance levels.
CMMC addresses the protection of FCI and CUI data:
- Federal Contract Information (FCI): Information not intended for public release. It is provided by or generated for the government under a contract to develop or deliver a product or service to the government. FCI does not include information provided by the government to the public.
- Controlled Unclassified Information (CUI): Information the government creates or possesses, or that an entity creates or possesses for or on behalf of the government, that a law, regulation, or government-wide policy requires or permits an agency to handle using safeguarding or dissemination controls.
Why CMMC Compliance Matters Right Now
CMMC compliance means meeting the Department of Defense's Cybersecurity Maturity Model Certification (CMMC) requirements for protecting sensitive government information. Built on a framework that primarily assesses implementation of NIST SP 800-171 controls, CMMC verifies, through self-assessment or independent review, that contractors have the cybersecurity controls in place to handle Federal Contract Information (FCI) and Controlled Unclassified Information (CUI).
CMMC compliance has moved from a future requirement to a present-day competitive filter. Recent research from the 2026 Deltek Clarity GovCon Study puts the shift in numbers:
59%
59% of contractors expect CMMC requirements to apply to their organization in 2026, up from 55% last year — 81% among the most AI-mature firms.
77%
77% of contractors overall plan an official, certified third-party CMMC assessment this year; that figure rises to 89% among AI-mature firms and 84% among Top Performers.
Source: 2026 Deltek Clarity GovCon Study
"For years, cybersecurity in government contracting was a checkbox exercise. Now it determines who can compete in the defense market. Firms without strong security and regulatory readiness risk losing access to valuable opportunities."
- Katie Arrington, Chief Information Officer, IonQ
How Will CMMC Impact Government Contractors?
Most organizations that fulfill government contracts for the DoD will need to address CMMC requirements in requests for information (RFIs) and requests for proposal (RFPs) bids for DoD acquisitions, with the potential exception for commercial items.
The various cybersecurity standards and best practices upon which CMMC is based are largely self-certified. CMMC represents a major change to that by introducing the C3PAO requirement to review systems and processes for Level 2 certification. To standardize this process, the DoD contracted with the non-profit, independent organization, Cyber-AB, to define the assessment and administration needed for certification. The Cyber-AB licenses and accredits assessors and firms that will serve as C3PAOs.
Government contractors will initially see DoD requirements to satisfy Levels 1 and 2 for anyone handling FCI or CUI.
The majority of contractors will need to certify first at Level 1 and then Level 2. Level 3 will be required for organizations working with the most sensitive CUI or confidential data; however, it will be required to first certify at Level 1 and Level 2 before Level 3.
Level requirements will be specified in contracts and are expected to flow down only to subcontractors that are working with the controlled information. In fact, 66% of contractors now report that CMMC compliance is required for subcontractors on their DoD contracts.
Therefore, it is important to know what type of data you are storing. Once an organization is CMMC certified, the certification is expected to be valid for three years.
Understanding CMMC Requirements
CMMC levels 1 and 2 map directly to NIST SP 800-171 controls. CMMC level 3 adds controls from NIST SP 800-172.
Level 1 – Foundational
Requires contractors and applicable subcontractors to verify through self-assessment that all applicable security requirements outlined in FAR clause 52.204-21 have been implemented.
Level 2 – Advanced
Requires contractors and applicable subcontractors to verify that all applicable security requirements outlined in NIST SP 800-171 Rev 2 and required via DFARS clause 252.204-7012 have been implemented.
As determined by DoD, program contracts will include either a CMMC Level 2 Self-Assessment requirement or a CMMC Level 2 Certification Assessment requirement to verify a contractor's implementation of the CMMC Level 2 security requirements.
Successful implementation requires meeting all objectives defined in NIST SP 800-171A for the corresponding CMMC Level 2 security requirements. A Certified Third-Party Assessment Organization (C3PAO) verifies this for contracts requiring third-party certification. The CMMC Level 2 Certification Assessment must be completed tri-annually, and the affirmation must be completed annually.
As Shenê Commodore, CEO of Commodore Consulting, frames it: "Cybersecurity...has always been a matter of these three things: how is the data protected at rest, how is the data protected in use, and how is the data protected in transmission."
Level 3 – Expert
Requires CMMC Level 2 C3PAO certification, plus additional NIST SP 800-172 security requirements and requires an assessment from the DCMA DIBCAC.
The CMMC Level 3 Certification Assessment must be completed tri-annually, and the affirmation must be completed annually.
What Does CMMC Compliance Cost?
Costs vary by organization size, certification level, and how much remediation is needed, but they are real and rising fast.
The 2026 Deltek Clarity GovCon Study puts numbers behind what contractors are actually spending:
- 46% of contractors report CMMC compliance costs of $100,000 to $249,999 to date.
- 32% expect costs of $250,000 to $499,999 over the next three years, and 37% expect costs to exceed $500,000.
- Firms that require CMMC project 18% growth in 2026 and 22% in 2027 — outpacing the 16%/19% projected across all contractors.
Source: 2026 Deltek Clarity GovCon Study
Is CMMC Phase 2 Suspended? What Changed in 2026
Yes, but only part of the program. On July 13, 2026, the Department of War suspended the rollout of CMMC Phase 2 and launched a 60-day review of the program. The November 10, 2026 deadline for third-party (C3PAO) Level 2 assessments is paused, and program offices can currently only require CMMC Level 1 or Level 2 self-assessments in new solicitations.
What hasn't changed: NIST SP 800-171 Rev 2 self-assessment remains mandatory for contractors handling CUI, DFARS 252.204-7012 stays fully enforceable, and FAR 52.204-21 (the Level 1 foundation) is unaffected. The Pentagon paused the third-party assessment mechanism — not the underlying obligation to be compliant.
For the full breakdown of what changed, what didn't, and what contractors should do during the review window, see Deltek's article on the CMMC Phase 2 suspension.
Guide
Get Your CMMC Readiness Guide
See what changed in CMMC, what Phase 2 means for your contracts, and how to close compliance gaps before your audit.
Important CMMC Terms You Need to Know
Assessors
Individuals who have successfully completed the background, training, and examination requirements as outlined by the CMMC Accreditation Body (AB), and to whom a license has been issued. Assessors are not employed by the CMMC-AB and may or may not be employed by the Certified Third-Party Assessment Organization (C3PAO).
Certified Third Party Assessment Organization (C3PAO)
An entity with which at least two assessors are associated and to which a license has been issued to engage with organizations seeking certification (OSC) to complete their associated CMMC assessment. For a closer look at what a certified assessment actually involves, see Deltek's guide to CMMC audits.
Cyber Accreditation Body (AB)
The accreditation body that establishes and oversees a qualified, trained, and high-fidelity community of assessors that can deliver consistent and informative assessments to participating organizations against a defined set of controls/best practices within the CMMC program.
Organizations Seeking Certification (OSC)
The organization that is going through the CMMC assessment process to receive a level of certification for a given environment.
Cloud Service Providers (CSP)
A third-party company offering a cloud-based platform, infrastructure, application, or storage services. CSPs may be storing sensitive unclassified information that is subject to CMMC certification.
How To Approach CMMC Certification
To prepare their organizations, government contractors should ensure they cover the following steps.
- Step 1: Identify and classify the type of data you store to support existing or new contract awards.
- Step 2: Understand the CMMC Level your firm will likely need to satisfy based on the type of data you store and identify the gaps that could prevent achieving certification.
- Step 3: If you are unsure and work with CUI, start with Level 2, based on the 110 controls from NIST SP 800-171.
- Step 4: Ensure you have documentation of formalized processes and controls.
- Step 5: Be familiar with the major definitions and compliance standards that make up CMMC.
Leveraging a Cloud Service Provider can be a solid strategy for addressing many aspects of CMMC. For instance, Deltek Costpoint GCCM has completed its FedRAMP Moderate Equivalency assessment and supports DFARS 252.204-7012 requirements and NIST SP 800-171 controls, which were adapted to form the basis of the CMMC framework. However, simply moving into the cloud does not automatically make a firm compliant, but it can assist with getting to certification quicker and at less cost.
For a step-by-step readiness plan, see Deltek's CMMC compliance checklist and its roadmap for navigating CMMC compliance.
Selecting a Cloud Service Provider
Here are 4 key considerations for government contractors when searching for the right cloud service provider solution:
- Evaluate whether they have a strong government contractor client base. This will ensure that the solution is tailored to meet your specific compliance requirements.
- Confirm your Cloud Service Providers (CSP) have achieved the FedRAMP Baseline Moderate or Equivalent standard. Learn more about how FedRAMP impacts CMMC compliance.
- Ask if they can demonstrate that the practices they will perform on your behalf meet the requirements of CMMC as a Cloud Service Provider (this cannot be inherited from a cloud infrastructure service such as AWS).
- Any Cloud Service Provider (CSP) working with CUI needs to have controls that align with DFARS clause 252.204-7012 (b)(2)(ii)(D), the FedRAMP Moderate baseline. See how a CSP supports CMMC compliance in practice.
How Deltek Supports Government Contractors With CMMC Requirements
Deltek builds governance and control into every product, so your cyber posture keeps pace with a constantly changing security landscape. That means ongoing investment in security, audit-readiness, and supporting technologies that ease and scale how your teams manage compliant systems.
"CMMC compliance is very much a priority for us because we are a Department of Defense contractor. It is of the utmost importance that we maintain all of our information to the top, most secure level. And Deltek has really helped with that because of their innovation and their forecasting of the compliance needs that are coming up in the future."
- Samantha Presser, HR Specialist, SURVICE
The DoD has mandated that all government contractors competing for DoD contracts are CMMC certified. Even with CMMC Phase 2 under review, many government contractors are treating CMMC readiness as a top priority to find a Cloud Service Provider (CSP) that offers a solution that will support their CMMC compliance requirements. Investing in a CSP and a solution that helps address all your requirements, including FedRAMP Moderate Authorization or Equivalency, is important.
Costpoint GCCM has completed its FedRAMP Moderate Equivalency assessment and is listed on the FedRAMP Marketplace, which delivers you the compliance support you will need for CMMC, with the understanding that compliance frameworks are a shared responsibility. At Deltek, we are dedicated to being that trusted partner. Deltek's government contracting compliance solutions extend this same governance and control across the rest of the project lifecycle.
Deltek Costpoint
The Leading ERP for GovCon and Defense Work
Costpoint connects project execution, finance, manufacturing, and procurement with embedded governance and compliance controls so you can manage mission-critical work..
Frequently Asked Questions About CMMC Compliance
CMMC stands for Cybersecurity Maturity Model Certification, a Department of Defense program that verifies contractors protect Federal Contract Information (FCI) and Controlled Unclassified Information (CUI). It is built on existing NIST SP 800-171 and NIST SP 800-53 standards. Most DoD contractors and applicable subcontractors must meet CMMC requirements to bid on and keep defense contracts.
Yes. On July 13, 2026, the Department of War suspended the CMMC Phase 2 rollout, which was set to require third-party (C3PAO) Level 2 assessments starting November 10, 2026. The suspension triggered a 60-day review, and during that window, program offices can only require CMMC Level 1 or Level 2 self-assessments. NIST SP 800-171 compliance remains mandatory throughout.
Most organizations that fulfill DoD contracts need to meet CMMC requirements, along with subcontractors that handle FCI or CUI. Requirements typically appear in requests for information and requests for proposal for DoD acquisitions. CMMC obligations also flow down the supply chain, so subcontractors working with controlled information often need their own certification.
CMMC has three levels. Level 1 (Foundational) requires self-assessment against FAR clause 52.204-21. Level 2 (Advanced) requires implementing NIST SP 800-171 controls, verified by self-assessment or a Certified Third-Party Assessment Organization depending on the contract. Level 3 (Expert) adds NIST SP 800-172 controls and a DIBCAC assessment for the most sensitive data.
Costs vary by organization size and certification level, but they are substantial and rising. Recent Deltek Clarity research found 46% of government contractors report CMMC compliance costs between $100,000 and $249,999 to date, and 37% expect costs to exceed $500,000 within three years. Though CMMC itself is only the assessment and validation, common drivers of this cost estimate include infrastructure upgrades, cybersecurity tooling, training, and continuous monitoring, all of which are essential for CMMC compliance assessment readiness.
No. CMMC does not replace NIST SP 800-171 requirements, it is built to assess the implementation of those controls. NIST SP 800-171 defines the security controls contractors must implement to protect CUI, while CMMC is the DoD certification program that verifies those controls are actually in place through self-assessment or third-party review.